Services / Infrastructure
Security
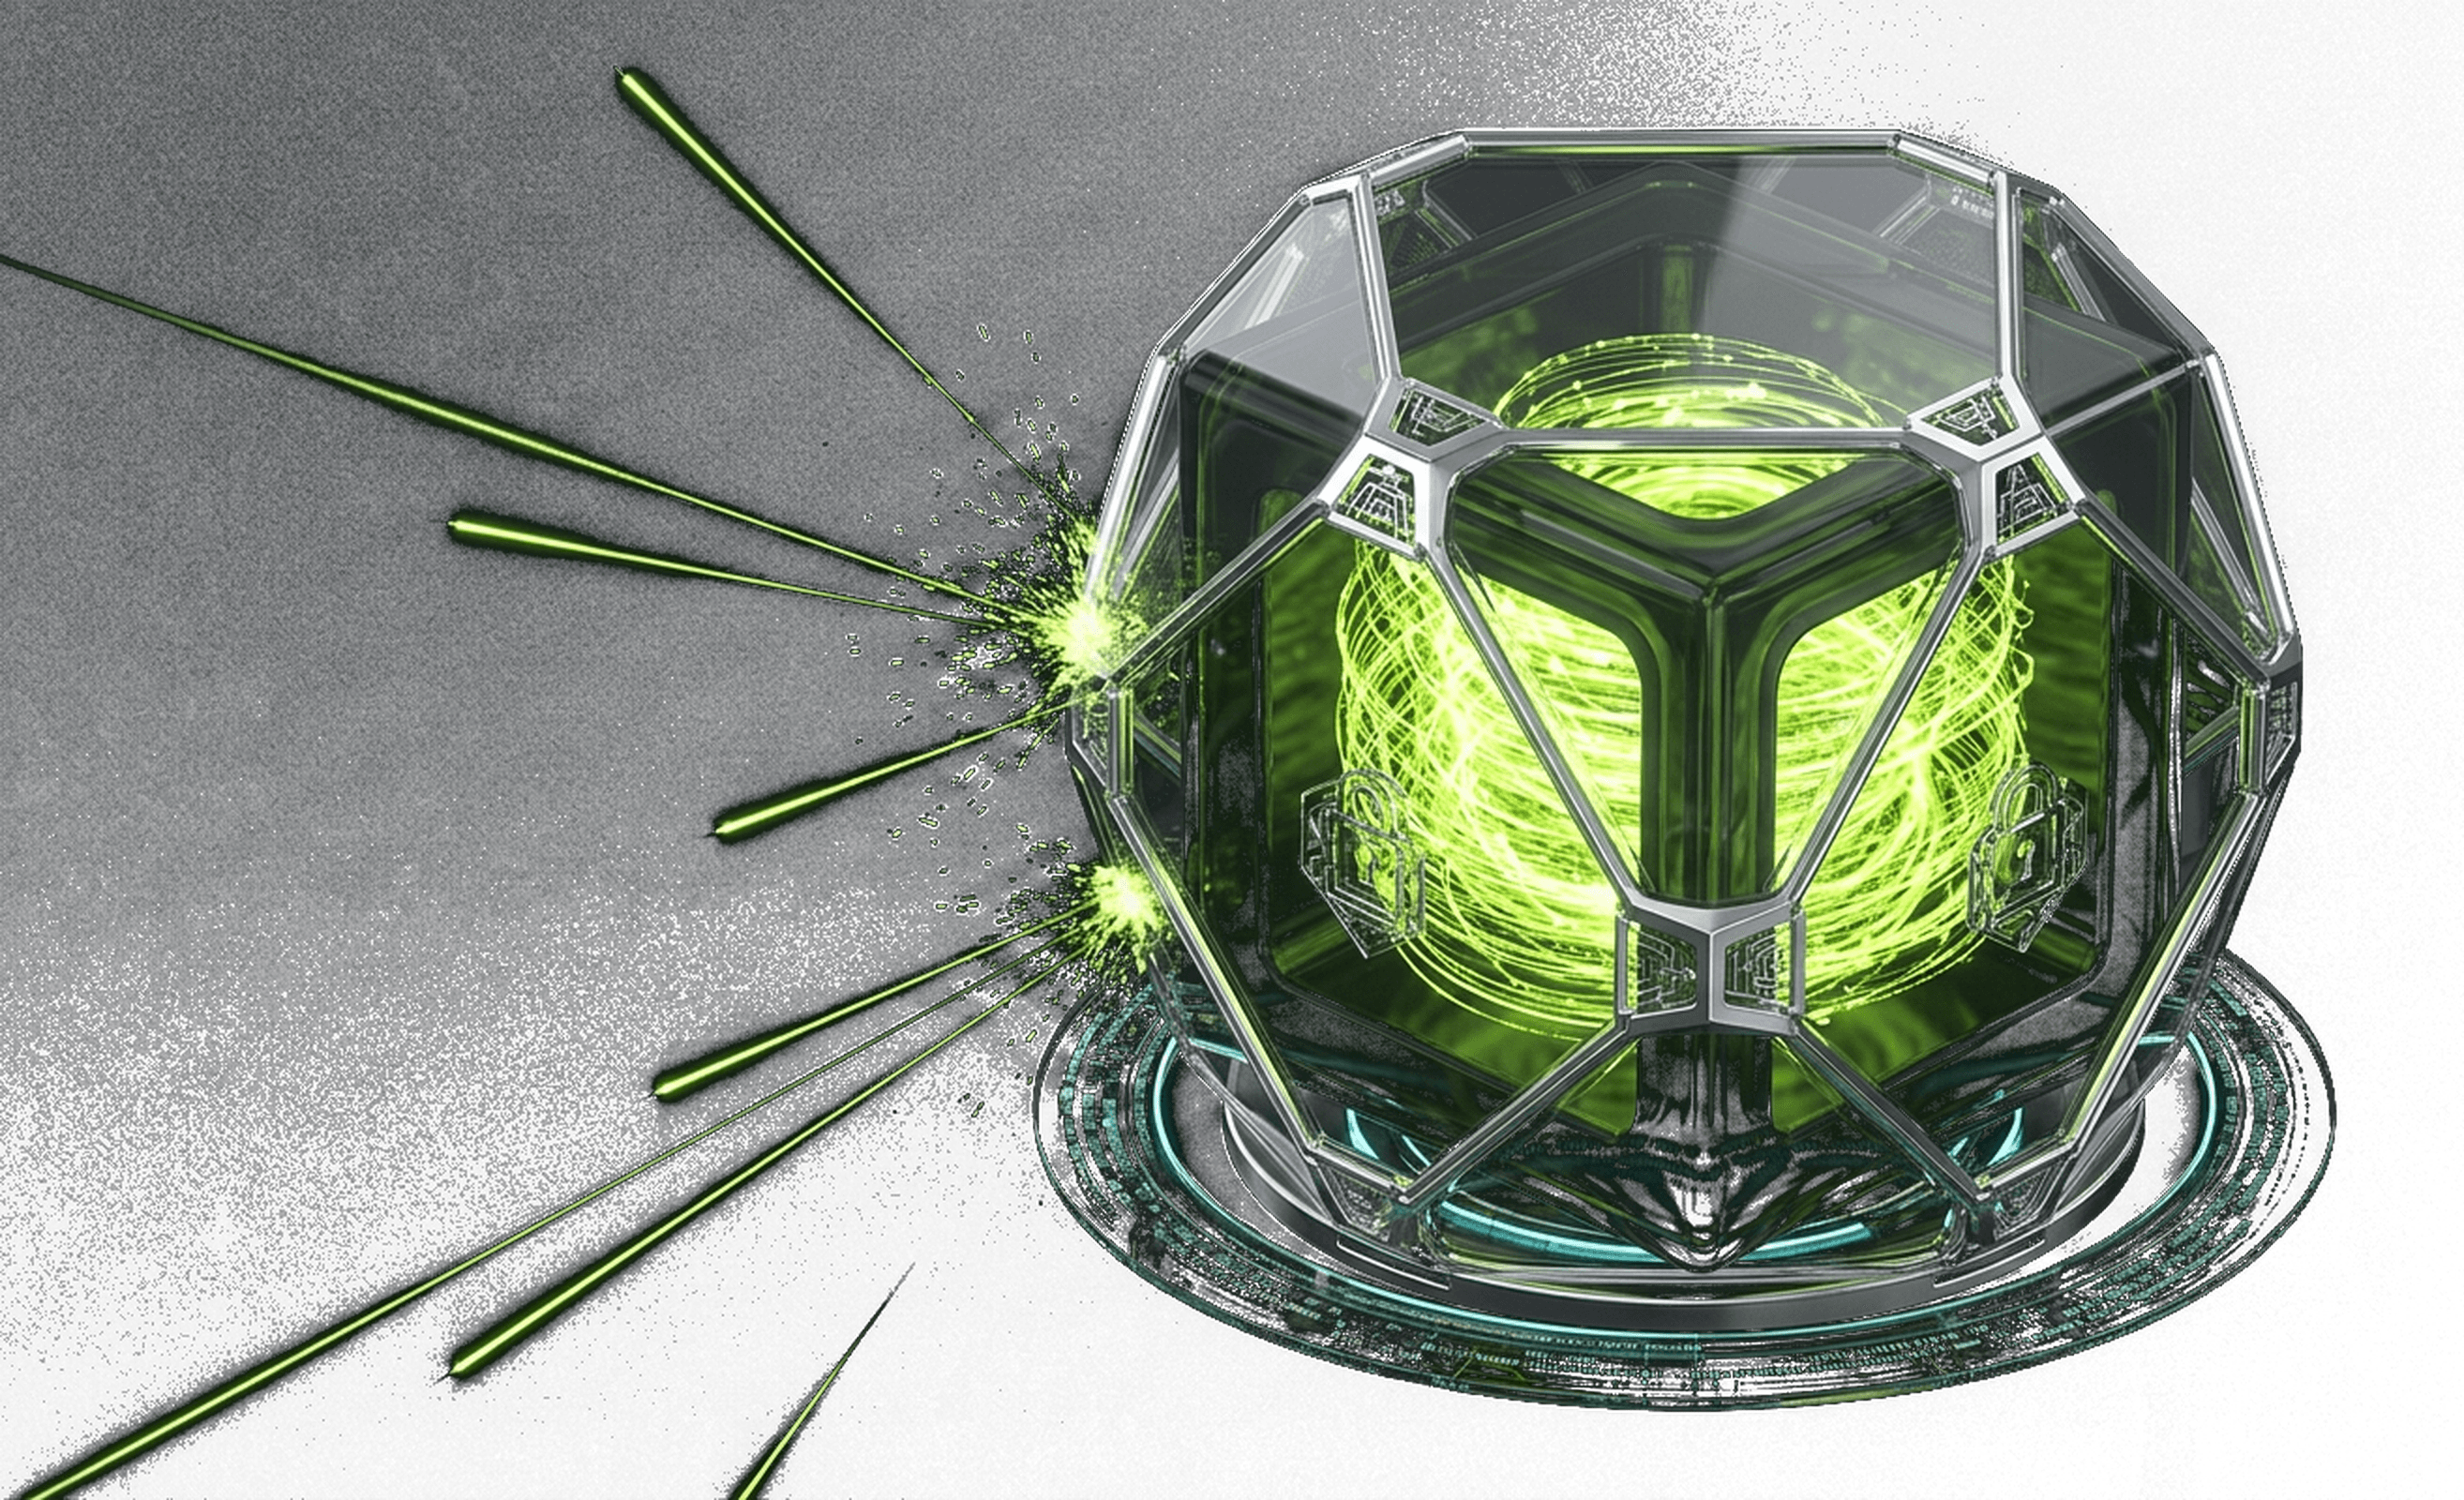
We set up and test your AI systems so company data never leaves, under permission and logging rules.
Security
Why it matters
AI touches an organization's most sensitive documents and systems. That is why we treat security not as a layer added later but as the first step of the installation: where data will live, who can reach what, what gets logged.
AI opens a new door
A misconfigured assistant can show a document to someone who should not see it.
A leak cannot be undone
Information that leaves the organization cannot be collected back.
Audits need evidence
Who did what, and when, must be answered with records.
There are new kinds of attacks
AI systems must be tested against attacks specific to them.
Security
What we do
Data residency
We identify and document where data lives and every route out.
Set up for KVKK
We set up the installation according to the requirements of KVKK, Turkey's personal data protection law, and document personal data flows.
Permission design
We connect user and application permissions to your corporate directory, so each user sees only their own area.
Logs and audit trail
We record who did what, and when, in tamper-proof logs.
Attack testing
We test against attacks specific to AI systems and prioritize the findings.
Hardened configuration
We tighten server, network and application settings on the principle of least privilege.
Security
How we work
 01
Discovery
We map systems, data flows and access.
 02
Risk assessment
We rank findings by impact and likelihood.
 03
Remediation
We fix permissions, logging and configuration.
 04
Testing and report
We verify with attack tests and report the results.
Security
What you have at the end
- An AI installation with documented data residency, permissions and logs.
- Prioritized findings and a remediation plan.
- A test report you can show in an audit.
Security
How we work with you
Scope agreed up front
We agree the architecture, scope and cost with you before work starts. What you plan is what you pay; no surprise items.
On-premise by default
Our default is your own servers. Data and models stay inside; every route out is documented.
On-site setup
When needed, our team is on site: placing the hardware, first boot, configuration and validation are done with you.
One team
The people who assess, install and operate are the same team. Knowledge is not lost in handovers.
We measure as we go
We test core workflows before every delivery and take a backup before every update.
We stay with you
After installation we keep operating it with monitoring, updates and support. The service level is written in the contract.
Security
FAQ
Is this only for Bizz AI products?
No. We also assess other AI systems in your organization.
Do the tests stop our systems?
We test within an agreed time and scope, without disrupting work.
Who fixes the findings?
We can fix them, or hand your team the remediation plan.
Security
Want to see it on your own servers?
We will show our products against your needs, using fictional data.